
Key takeaway
A CDN caches public assets near visitors; the origin server renders HTML, checks permissions, handles forms, and sets cache rules; and object storage isolates uploads from code deploys. Keep immutable hashed assets separate from revalidated HTML and no-store private routes.
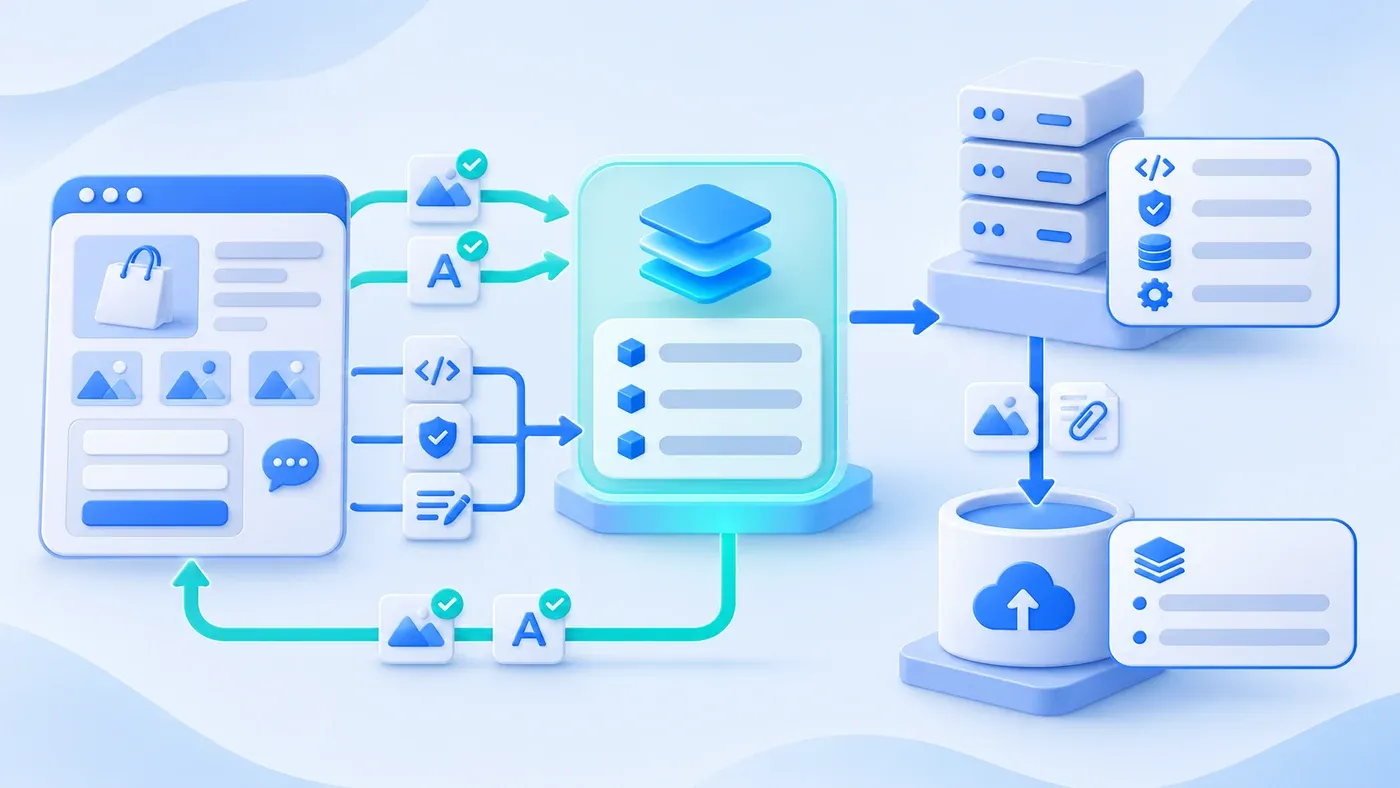
When business owners review a website proposal or cloud invoice, three terms almost always appear together: CDN, origin server, and object storage (or a persistent upload volume). Proposals often gloss over them as "a server plus a CDN," yet mixing up these three layers triggers painful post-launch surprises: an editor fixes a product spec and still sees yesterday's copy two hours later, overwrites a diagram only to find visitors stuck on the old graphic, or deploys a template update that wipes weeks of uploaded case images.
Here is the clean rule of thumb: a CDN edge node caches public assets close to visitors; the origin server renders HTML, verifies login and draft-preview permissions, handles forms, and sets cache headers; and object storage (or an isolated persistent volume) safeguards uploaded media and downloads separately from code deploys. Keeping those boundaries sharp—while separating content-hashed static files from dynamic HTML and private endpoints—keeps your website both fast and safe.
Tracing One Page Visit: What Each Layer Handles
- CDN: public-content caching
- Origin: application and access
- Storage: persistent media
- Delivery: coordinate versions and caches
Imagine a prospective buyer clicking a link to open a product detail page with updated specifications, custom web fonts, product photos, a PDF datasheet, and a consultation form. Their requests flow through three distinct stops:
- CDN Edge Nodes (Closest Public Delivery & Shared Cache) Requests first hit the nearest CDN edge node, cutting cross-province or cross-ocean latency (a major factor when serving overseas markets alongside domestic regions, as outlined in our Multilingual & Standalone Global Site Solutions). Under MDN Web Docs' HTTP caching terminology, a CDN acts as a shared cache: it stores one public response and reuses it across many visitors. It handles public static asset delivery, nearby TLS termination, and explicitly shareable pages—not your database, login authentication, or form writes.
- Application Origin Server (Rendering, Permissions & Cache Policy) Requests that miss the edge cache—or cannot be shared—travel back to the application origin server. The origin owns four jobs: rendering fresh HTML from the database; checking session cookies for
/adminlogins or unpublished draft previews; validating and storing form submissions (POST); and attachingCache-ControlandETagheaders that tell CDNs and browsers what may be cached and when to revalidate. - Object Storage or Persistent Upload Volume (Media Separated from Code) Once HTML arrives, the browser requests uploaded product photos and PDF brochures. Daily CMS uploads belong in object storage (an isolated cloud bucket) or a dedicated persistent volume, fronted by your CDN or clean delivery routes. Application code is rebuilt and replaced via Git deployments; isolating uploads from ephemeral app containers or build folders ensures code deploys and rollbacks never delete live media.
Two Caching Accidents That Break Accuracy and Privacy
Even with all three layers running, sloppy Cache-Control rules cause two notorious failures. Consider a hypothetical scenario: before an industry expo, an equipment maker updates product lead times in its CMS and re-uploads a corrected technical diagram, while an editor simultaneously opens an unpublished draft via a preview cookie.
- Accident 1: Long CDN Caching on Dynamic HTML or Preview-Cookie Pages Adding multi-hour CDN cache rules across every URL—including HTML—without reliable publish-triggered invalidation triggers two failures. First, edits stall: the database updates immediately, yet visitors read outdated specs for hours until the edge TTL expires. Second, private previews can leak: if the origin forgets
no-storeorprivateon cookie-gated draft previews, MDN explicitly warns that shared caches can save an authenticated response and reuse it for anonymous visitors hitting the same URL. - Accident 2: Overwriting an Image at the Same URL Without a Content Hash Suppose the team replaces the diagram at the exact same filename (
/uploads/device-diagram.webp), which previously shipped with a longmax-age. The editor hard-refreshes and sees the fix, yet buyers still see the wrong chart. Per web.dev's HTTP Cache guide and MDN, browsers skip network checks completely while a file remains fresh—and no HTTP response directive exists to remotely purge already-stored copies from intermediate caches. Even after manually purging the CDN console, repeat visitors keep seeing the cached file locally untilmax-ageexpires.
Setting Cache-Control by Asset Type: Hashes vs. Revalidation
Both MDN and web.dev emphasize a crucial baseline: omitting Cache-Control does not disable caching—browsers and proxies fall back to heuristic guessing instead. Split responses explicitly into three tiers:
1. Content-Hashed Static Assets: Long-Lived immutable Cache When build pipelines or media processors embed a fingerprint or version into each static asset URL (the cache-busting pattern, such as hero-800w.c387d6ef.webp), any byte change generates a new URL. Pair those immutable URLs with a one-year lifetime (31,536,000 seconds) and immutable so reloading visitors skip needless revalidation:
Cache-Control: public, max-age=31536000, immutable2. Public HTML & Unversioned URLs: no-cache Revalidation or Short Controlled Edge TTL Readable page URLs like /en/services/website cannot append random hashes on every typo fix. Start from a reliable revalidation baseline:
Cache-Control: no-cacheDespite its name, no-cache does not mean "do not cache." As MDN and web.dev clarify, it lets caches store the HTML but forces revalidation with the origin before every reuse. Paired with a content-based ETag (If-None-Match), unchanged pages return a tiny 304 Not Modified, while edited pages immediately serve fresh HTML pointing to updated image hashes. High-traffic sites needing brief edge caching can apply s-maxage (and optionally stale-while-revalidate) only with publish-purge hooks and cookie bypass rules in place.
3. Admin Routes, Draft Previews & Form APIs: no-store /admin dashboards, cookie-authenticated draft previews, and consultation submission endpoints (POST) must never touch shared caches or disk storage:
Cache-Control: no-storePer MDN, no-store forbids both CDNs and browsers from storing any copy (use private if single-user local caching is explicitly intended). Avoid piling redundant flags like private, no-cache, no-store, max-age=0, must-revalidate together—no-store alone states the policy cleanly.
CDN, Origin Server, and Object Storage Duties & Cache Policies
Layer & Asset Class | Core Responsibility | Auth & Writes? | Recommended | Misconfiguration Consequence |
|---|---|---|---|---|
CDN Edge (Hashed Static Assets) | Serve fingerprinted image derivatives, font subsets, bundled CSS/JS near visitors | No; public read acceleration | | Applying |
CDN Edge (Public HTML / Unhashed Files) | Proxy requests; optionally cache public HTML briefly when purge hooks exist | No; must bypass on auth/preview cookies | Default | Long TTL without purge freezes edits on live pages or risks caching gated previews |
Origin Server (HTML, Auth & APIs) | Render dynamic HTML, validate login/preview cookies, process forms, emit headers | Yes; sole auth & write authority | Public HTML: | Missing |
Object Storage / Persistent Volume | Store CMS uploads, web derivatives, and public PDFs outside code deploys | Origin-controlled writes; CDN-fronted reads | Emit new hashed/versioned paths on upload before long caching; no long TTL on overwrites | Storing uploads inside ephemeral containers or code folders loses media on deploy |
Website Storage & Caching Handoff Checklist
Use this checklist to verify infrastructure boundaries with your engineering or operations team before launch:
[Website Storage & Caching Handoff Checklist]

1. Storage & Deployment Isolation
- [ ] Git holds only application code and templates; CMS uploads and downloadable files live in isolated object storage or a persistent volume verified across code redeploys and restarts
- [ ] Inquiries, admin settings, and unpublished drafts require origin authentication and never sit in a public media bucket

2. Versioned Static Naming & Long Cache Rules
- [ ] Web image derivatives, font subsets, and bundled JS/CSS embed content hashes or version tokens so edits change the URL
- [ ] `Cache-Control: public, max-age=31536000, immutable` applies exclusively to hashed or versioned URLs
- [ ] Fixed overwrite URLs (e.g., permanent datasheet links) avoid `immutable` and use short TTLs or revalidation

3. HTML, Preview Cookie & API Safeguards
- [ ] Every public page and API route sends an explicit `Cache-Control` header rather than relying on browser heuristics
- [ ] `/admin`, draft previews, logged-in views, and form endpoints emit `Cache-Control: no-store`
- [ ] CDN rules bypass shared caching whenever session or preview cookies are present

4. Pre-Launch DevTools & Incognito Checks
- [ ] Verify `Cache-Control` and `ETag` headers in **Network → Doc** (`no-cache` / `304 Not Modified` on reload) and long `immutable` headers on hashed assets
- [ ] Publish a copy edit plus image swap, then open the URL in a fresh Incognito tab to confirm both update immediately
- [ ] Open a CMS draft preview URL in an unauthenticated Incognito tab to confirm access is denied and no shared cache headers appear
Clarifying what your CDN, origin server, and object storage each manage keeps page speed, safe code deploys, and instant content updates working together instead of colliding. If you are planning a bilingual website build or pre-launch handoff, review our Corporate Website & Standalone Site Services and Delivery Process, or bring your hosting and caching setup to our consultation page to map out the right boundaries.
